


Services
- Home
- Services
Our Services
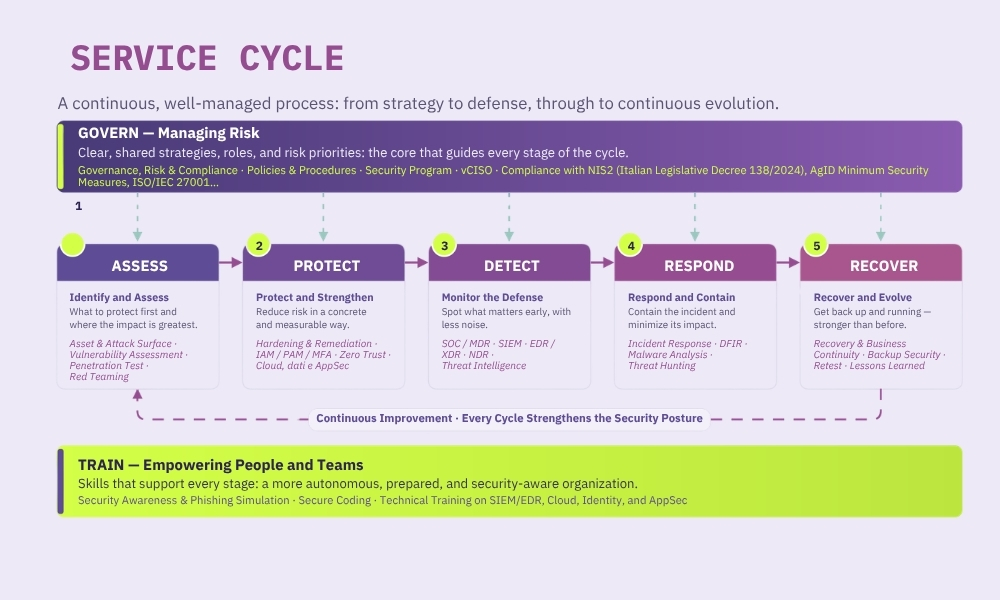
Cyberlab 3.26’s offering is structured around six pillars, each designed to deliver a clear and tangible outcome for the client.
The technical areas outlined under each pillar define the scope of the service, while the delivery model—directly, through partnerships or as part of a temporary consortium—is determined according to the project, its scope and the client’s level of maturity.
- GOVERN RISK
We help organisations turn cybersecurity into clear decisions, sustainable priorities and well-defined responsibilities. We support the development of cybersecurity governance frameworks, improvement roadmaps and investment criteria, taking into account the organisation’s mission, regulatory obligations and operational risk.
Key Areas
Governance, Risk & Compliance; Policies; Procedures; Security Programmes; Cybersecurity governance support, including through a vCISO model. - IDENTIFY AND ASSESS
We build a reliable picture of assets, exposure and security gaps to determine what should be protected first and where action can have the greatest impact. We assess scope, configurations, vulnerabilities and the resilience of infrastructures, identities, cloud environments and applications.
Key Areas
Cyber Risk Assessment; Security Assessment; Vulnerability Assessment; Asset Inventory; CMDB; Attack Surface Management (ASM); Active Directory, cloud and network assessments; Penetration Testing; Red Teaming. - PROTECT AND STRENGTHEN
We design and implement security measures that deliver tangible risk reduction, including hardening, remediation, and the protection of identities, data, workloads, portals and exposed services. The goal is to improve business continuity, access control and technical resilience.
Key Areas
Identity and Access Management (IAM, PAM, MFA, Zero Trust); Data, Workloads and Cloud Security (Cloud Security, Data Security, Backup Security, system and service hardening); Application Security and Software Supply Chain Security (Application Security, WAF/WAAP, Secure Code Review, SAST, DAST, SCA, SBOM). - MONITOR AND DEFEND
We deploy continuous defensive capabilities to detect meaningful signals, reduce noise and prioritise what truly matters.
Key Areas
Security Monitoring; SecOps; Blue Teaming; SOC/MDR; SIEM; EDR/XDR; NDR; IDS/IPS; Threat Intelligence; Detection Engineering; Security Dashboards; SOAR. - RESPOND AND RECOVER
When an incident occurs, we help contain, analyse and coordinate the response, restoring services while reducing operational impact and recovery times. Every event also becomes an opportunity to address root causes, verify the effectiveness of the measures taken, and improve processes and playbooks.
Key Areas
Incident Response; DFIR; Malware Analysis; Threat Hunting; Containment; Escalation; Recovery; Business Continuity; Retesting; Reporting. - TRAIN PEOPLE AND TEAMS
We strengthen the awareness, technical capabilities and decision-making readiness of users, IT teams, administrators, key contacts and management.
Security does not depend on technology alone, but also on the people who use and manage it every day. For this reason, training is integrated into every stage of the cybersecurity journey, from assessment to remediation and from monitoring to incident management, with the aim of making the organisation more autonomous, prepared and security-aware.
Key Areas
Security Awareness; Phishing Simulations; Secure Coding; Technical Training on SIEM, EDR and other advanced security tools; Cloud Security; Identity Security; Application Security.
I nostri servizi
L’offerta di Cyberlab 3.26 è articolata in sei pilastri, ciascuno orientato a un esito riconoscibile per il cliente. Gli ambiti tecnici indicati per ciascun pilastro descrivono l’estensione del servizio, mentre le modalità di erogazione — diretta, in partnership o tramite RTI — vengono definite in base al progetto, al perimetro e al livello di maturità del cliente.
Aiutiamo l’organizzazione a trasformare la cybersecurity in decisioni chiare, priorità sostenibili e responsabilità definite. Supportiamo la definizione della governance cyber, della roadmap di miglioramento e dei criteri di investimento, tenendo conto di missione, obblighi normativi e rischio operativo.
AMBITI CHIAVE
Governance, Risk & Compliance; Policy; Procedure; Security Program; Affiancamento alla governance cyber anche in modalità vCISO.
Costruiamo una fotografia affidabile di asset, esposizione e gap, per capire cosa proteggere prima e dove intervenire con maggiore impatto. Verifichiamo perimetro, configurazioni, vulnerabilità e resilienza di infrastrutture, identità, cloud e applicazioni.
AMBITI CHIAVE
Cyber Risk Assessment; Security Assessment; Vulnerability Assessment; Asset Inventory, CMDB, Attack Surface Management (ASM); Assessment di Active Directory, cloud e rete; Penetration Test; Red Teaming.
Progettiamo e attuiamo misure di sicurezza che riducono il rischio in modo concreto: hardening, remediation, protezione di identità, dati, workload, portali e servizi esposti. L’obiettivo è aumentare continuità operativa, controllo degli accessi e resilienza tecnica.
AMBITI CHIAVE
Identità e accessi (IAM, PAM, MFA, Zero Trust); Dati, workload e cloud (Cloud Security, Data Security, Backup Security, hardening di sistemi e servizi); Sicurezza applicativa e software supply chain (Application Security, WAF/WAAP, Secure Code Review, SAST, DAST, SCA, SBOM).
Mettiamo in esercizio capacità difensive continue per intercettare segnali utili, ridurre il rumore e dare priorità a ciò che conta davvero.
AMBITI CHIAVE
Security Monitoring, SecOps, Blue Teaming, SOC/MDR, SIEM, EDR/XDR, NDR, IDS/IPS, Threat Intelligence, Detection Engineering, Dashboard, SOAR.
Quando si verifica un incidente aiutiamo a contenere, analizzare, coordinare e rimettere in esercizio i servizi, riducendo impatto operativo e tempi di recupero. Ogni evento diventa anche un’occasione per correggere cause radice, verificare l’efficacia degli interventi e migliorare processi e playbook.
AMBITI CHIAVE
Incident Response, DFIR, Malware Analysis, Threat Hunting, Contenimento, Escalation, Recovery, Business Continuity, Retest, Reporting.
Formare persone e team.
Rafforziamo consapevolezza, capacità tecniche e prontezza decisionale di utenti, IT, amministratori, referenti e direzione. La sicurezza non dipende solo dalla tecnologia, ma da chi la utilizza e la gestisce ogni giorno. Per questo la formazione accompagna ogni percorso, dall’assessment alla remediation, dal monitoraggio alla gestione degli incidenti, con l’obiettivo di rendere l’organizzazione più autonoma, preparata e consapevole.
AMBITI CHIAVE
Awareness, Phishing Simulation, Secure Coding, Training tecnico su SIEM/EDR ed altri tool di sicurezza avanzata, cloud, identity e AppSec.
Every engagement begins with an initial discussion and develops progressively, leading to the delivery of evidence, actions and practical tools that support continuous improvement.
Initial Discussionon
Definition of objectives, scope, critical issues and service levels.
Rules of Engagement and Evidence Collection
Collection of essential documentation and integration of log sources, tools and dashboards.
Assessment or Operational Services
Launch of the technical and organisational activities included in the engagement.
Findings and Action Plan
Presentation of technical evidence, an executive summary and a structured action plan.
Follow-up and Continuous Improvement
Assisted remediation, ongoing support, retesting and managed services.

Ogni percorso nasce da un confronto iniziale e si sviluppa in modo progressivo, fino alla restituzione di evidenze, azioni e strumenti utili al miglioramento continuo.
Confronto iniziale
Definizione di obiettivi, perimetro, criticità e livelli di servizio.Regole d’ingaggio e raccolta evidenze
Raccolta della documentazione essenziale, integrazione di fonti log, strumenti e dashboard.Assessment o servizi operativi
Avvio delle attività tecniche e organizzative previste dal percorso.Restituzione e piano d’azione
Condivisione di evidenze tecniche, sintesi executive e piano di intervento.Follow-up e miglioramento progressivo
Remediation assistita, supporto continuativo, retest e servizi gestiti.Delivery Models and Service Lifecycle
Not an off-the-shelf service, but a modular lifecycle tailored to each client’s maturity, complexity and criticality. The same lifecycle can be delivered through three models:
- PROJECT · DIRECT ENGAGEMENT
Clearly defined objectives, timelines and deliverables, including assessments, roadmaps, remediation, hardening and training. - PROGRAMME · PARTNERSHIPS AND TEMPORARY CONSORTIA
Tenders, framework agreements and multi-vendor initiatives managed under a single coordination structure with shared governance. - MANAGED SERVICE · SOC/MDR
Monitoring, triage, tuning and incident management, with SLAs up to 24/7 coverage.
Whether delivered as a targeted engagement, a structured programme or an ongoing managed service, the goal remains the same: cybersecurity that is governed, measurable and able to evolve over time.
Modelli di erogazione e ciclo di servizio
Non un servizio preconfezionato, ma un ciclo modulare che si adatta a maturità, complessità e criticità di ogni cliente. Lo stesso ciclo, erogato in tre modi:
Obiettivo, tempi e deliverable definiti: assessment, roadmap, remediation, hardening, formazione.
Gare, accordi quadro e iniziative multi-fornitore, sotto un’unica regia con governance condivisa.
Monitoraggio, triage, tuning e gestione incidenti, con SLA fino al 24/7.
Intervento puntuale, programma o presidio continuativo: l’obiettivo è sempre una cybersecurity governata, misurabile e capace di evolvere.
Key Differentiators
What Sets Us Apart:
- Evidence, not opinions — verifiable outputs, including reports, action plans and retesting, with priorities based on actual risk.
- Governance and technology working together — no gap between regulatory compliance and effective protection.
- Technology-neutral approach — we first maximise the value of your existing technologies, then integrate open-source tools, commercial solutions and partners according to a minimum-impact principle.
- We help implement, not merely advise — regulations and standards define the requirements, while frameworks indicate how to meet them. We select, implement and demonstrate the most appropriate approach. Our references include NIS2 (Italian Legislative Decree 138/2024), AgID Minimum Measures, ISO/IEC 27001, NIST CSF 2.0, CIS Controls, OWASP, MITRE ATT&CK and others.
- A service tailored to your organisation — direct engagement, partnerships, temporary consortia or managed services: you choose the delivery level, and we adapt to your scope, SLAs and maturity.
Elementi qualificanti
Cosa ci distingue:
Evidenze, non opinioni — output verificabili (report, piani, retest) e priorità basate sul rischio reale.
Governance e tecnica insieme — nessuna frattura tra adempimento normativo e protezione che funziona.
Technology-neutral — valorizziamo prima ciò che hai già; integriamo open source, soluzioni commerciali e partner secondo il principio del minor impatto.
Aiutiamo a realizzare, non solo a indicare — normativa e standard fissano l’obbligo, i framework dicono il come; noi scegliamo, implementiamo e dimostriamo. Riferimenti: NIS2 (D.Lgs. 138/2024), MM AgID, ISO/IEC 27001, NIST CSF 2.0, CIS Controls, OWASP, MITRE ATT&CK, ecc.
Il servizio si adatta a te — diretto, partnership, RTI o gestito: scegli il livello, noi ci modelliamo su perimetro, SLA e maturità.
Evidenze, non opinioni
Soluzioni digitali per semplificare i processi, migliorare l’accesso ai servizi e rendere la giustizia più efficiente.
Sicurezza
Soluzioni digitali per proteggere i dati, prevenire minacce informatiche e garantire la sicurezza dei sistemi pubblici.
Sicurezza
Soluzioni digitali per proteggere i dati, prevenire minacce informatiche e garantire la sicurezza dei sistemi pubblici.
Sicurezza
Soluzioni digitali per proteggere i dati, prevenire minacce informatiche e garantire la sicurezza dei sistemi pubblici.
Sicurezza
Soluzioni digitali per proteggere i dati, prevenire minacce informatiche e garantire la sicurezza dei sistemi pubblici.
Follow us to stay up to date with all our activities